Adversary Research
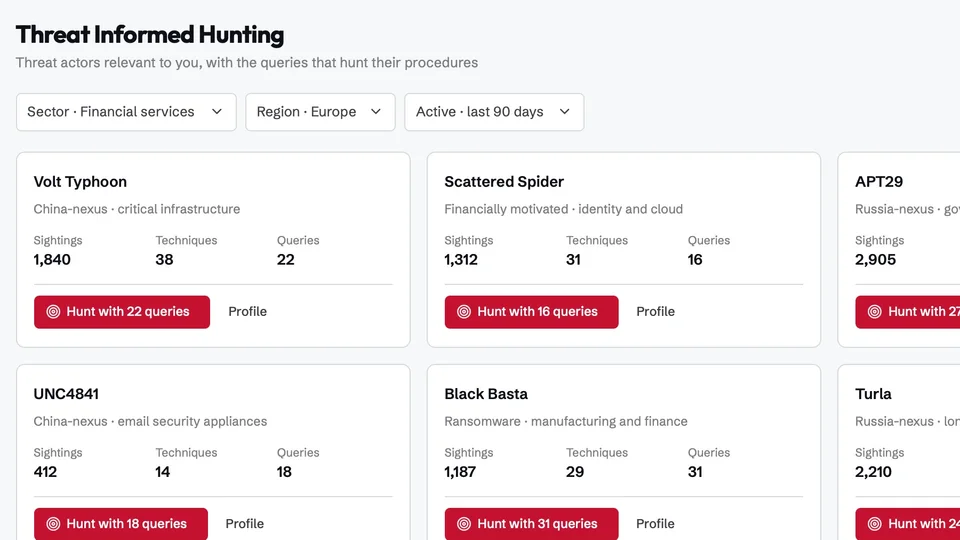
We study how attackers operate. Malware analysis, breach investigation, and TTP development inform the simulations and detections we build.
About Crimson7
Our research informs what we test. Validation shows what holds up. Engineering turns the findings into defenses teams can use.
Why we exist
Attackers do not separate testing, detection, and response. We connect those disciplines through C7 Platform and specialist services, helping teams see where defenses hold, where they fail, and what to improve next.
What we do
Research shapes the scenarios. Simulations test the defenses. Engineering and operations turn the result into a practical next step.
We study how attackers operate. Malware analysis, breach investigation, and TTP development inform the simulations and detections we build.
We replicate adversary behavior. Red team exercises, purple team programs, and continuous validation test your defenses against how threats actually work.
We build defensive capability. Detection rules, hunting queries, and response playbooks, delivered as code, validated against real attacks.
We extend your team. Managed services that integrate with your SOC, providing expertise without overwhelming your operations.
How we work
The people
Researchers, engineers, operators, and leaders working across the platform and our services.
CEO

CTO
Board Advisor
Director of Marketing

Director of Engineering

Head of Professional Services

Head of HEI & Compliance

Lead Researcher
Join Us
Let's discuss your security challenges and how our approach might help. Or if you're looking for a career in offensive security, explore our open positions.